Qubes OS: Security Through Isolation
Qubes OS compartmentalizes a desktop into isolated virtual machines, so that one compromise does not take the whole system with it.
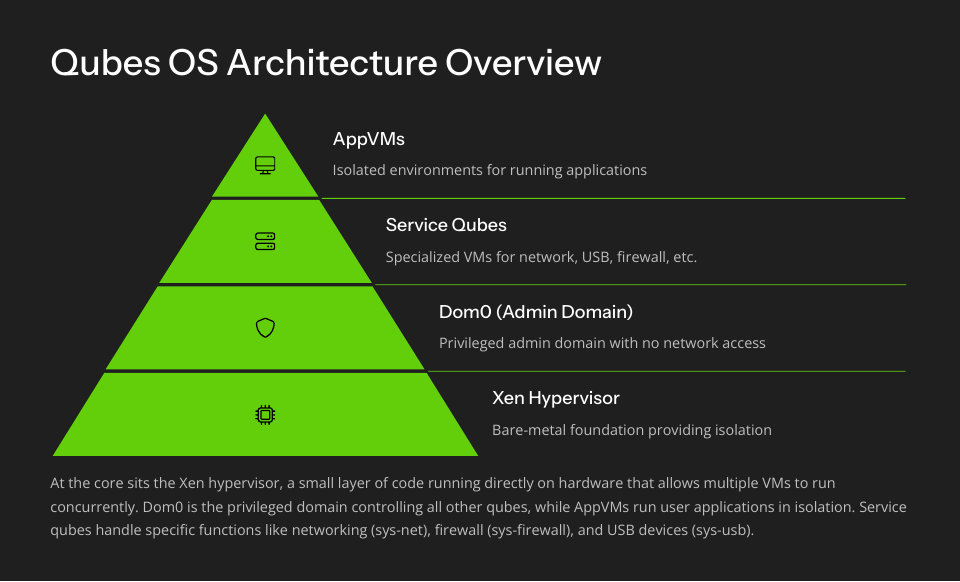
Qubes does not try to make one operating system harder to break into. It assumes
something will eventually be broken into and arranges for that to matter less.
The isolation is enforced by the Xen hypervisor using the hardware
virtualization extensions, and dom0, the administrative domain that manages
every other qube, has no network access at all.
The storage design is what makes it usable rather than merely secure. AppVMs
share read-only templates through LVM thin provisioning with copy-on-write
overlays, so a dozen qubes cost far less disk than a dozen virtual machines
would. Only /home persists. Everything else you change inside an AppVM is gone
at shutdown, which is either the point or an irritation, depending on what you
were doing at the time.
The cost is real and worth saying out loud. It wants a lot of hardware, there is overhead, and it asks you to decide in advance which parts of your life belong in which qube. That last one is not a technical problem and no amount of isolation will solve it. A perfectly compartmentalized system, used carelessly, is just a slow laptop.
It earns its keep for people whose threat model justifies the trouble: developers isolating work environments, security people opening malware on purpose, journalists protecting sources, and anyone who would rather their banking and their browsing did not share an address space.